Applied Gen AI Security Engineering Program
Applied Gen AI Security Engineering Program is a six-month program: a four-month, sixteen-week enterprise AI security journey built around seven progressive capability modules and a hands-on lab-based learning path, followed by two months of project work. A six-month Employment Training Program is available after that as an add-on. It carries learners from an accurate understanding of how AI and LLM systems actually behave through to threat-modeling, authorised testing, defending, and governing production-grade enterprise AI systems.
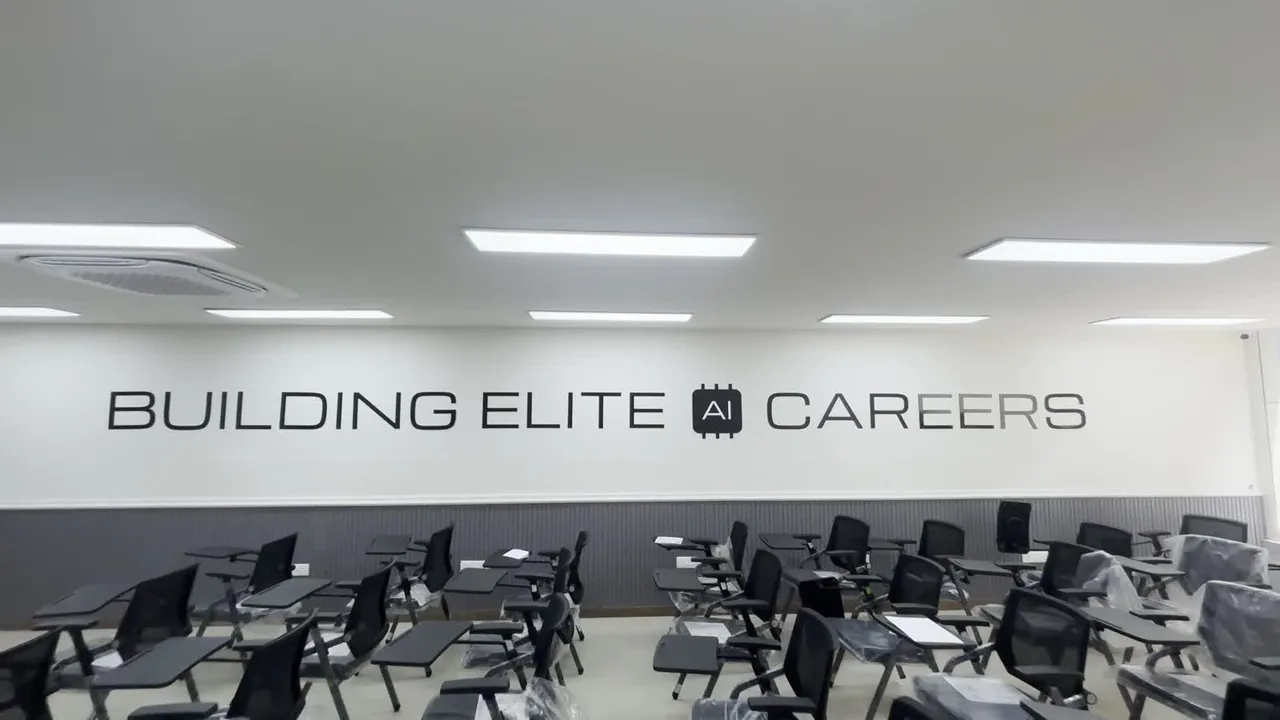
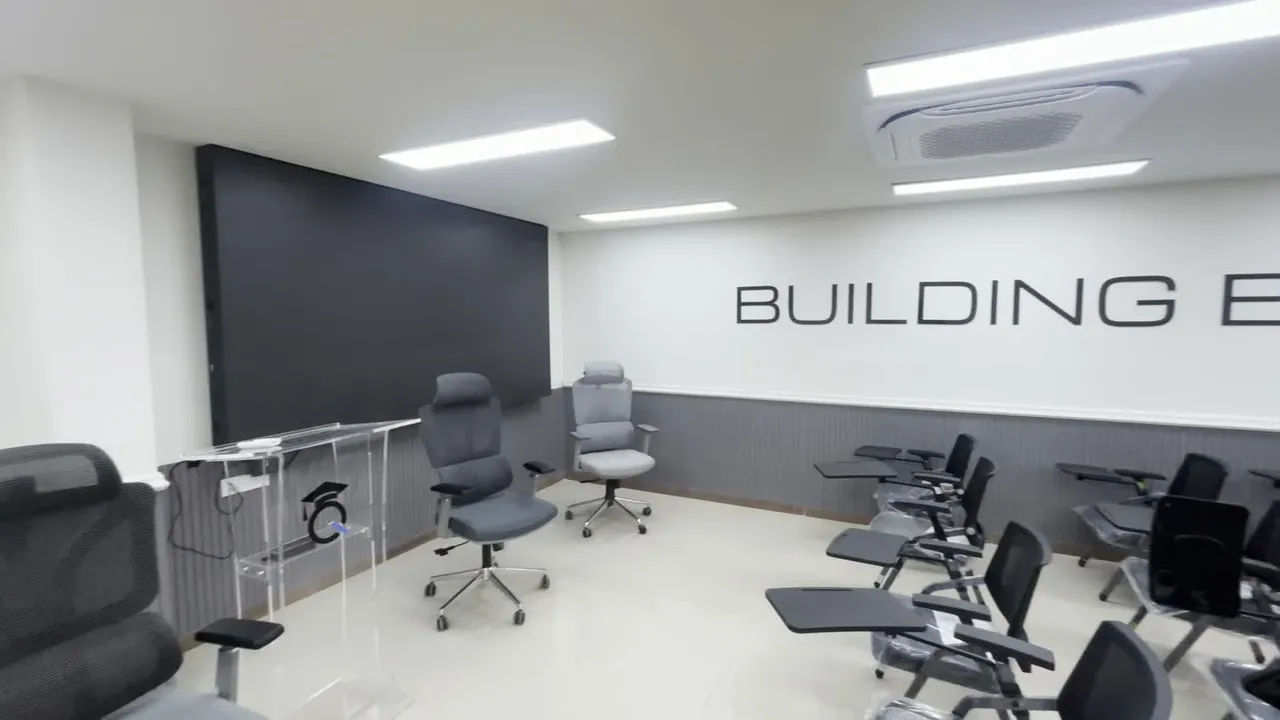
Taught in person at Jubilee Hills, Hyderabad. How to reach us
The curriculum
Foundation
No prior AI security experience is assumed at the start of the program. Learners first build an accurate understanding of how AI and LLM systems behave, then establish the cybersecurity and enterprise-architecture foundation needed to secure them: trust boundaries, RAG and retrieval security, conversation memory, data handling and API security. This foundation supports every assessment and governance stage that follows.
Applied Assessment & Defense
The core assessment build-out: agentic AI and MCP security, structured threat modeling, authorised adversarial testing, and the detection and defensive engineering needed to close what testing reveals.
Enterprise Governance & Capstone
Enterprise integration: using AI responsibly to support security operations, translating technical evidence into governance and assurance decisions, and a two-week capstone that ties every capability into one defensible enterprise AI security assessment.
Week by week
Sixteen teaching weeks in eight modules. Open a week to see its focus, the learning areas, the applied exercise and the professional outcome.
AI, LLM & Cybersecurity Foundations
Building accurate mental models of AI and LLM behaviour and core cybersecurity principles as the shared foundation for enterprise AI security.
FocusEstablish an accurate technical understanding of how AI, machine learning and large language models actually behave: the shared vocabulary the rest of the program builds on for security work.
Key learning areas- Artificial intelligence, machine learning and generative AI concepts relevant to security practice
- Foundation models and the current landscape of open versus closed, frontier versus efficient systems
- LLM behaviour: tokens, context windows, inference and embeddings
- How prompts and instructions shape model output
- Non-determinism, hallucination and their security implications
- Where generative AI genuinely changes an organisation's risk profile
A guided, controlled-environment exploration observing baseline model behaviour and comparing how system and user instructions are processed.
Learners can explain how an LLM actually behaves, in both business and technical language, as the foundation for evaluating its security.
FocusConnect core cybersecurity principles to the architecture of an enterprise AI system, establishing the trust-boundary vocabulary used for the rest of the program.
Key learning areas- Confidentiality, integrity and availability applied to AI-enabled systems
- Identity, authentication and authorisation fundamentals for AI workflows
- Enterprise AI architecture: components, data flows and integration points
- Trust boundaries and initial attack-surface awareness
- Mapping familiar web and API security concepts onto AI-enabled applications
- Security responsibilities across the AI system lifecycle
A guided architecture walkthrough identifying assets, trust boundaries and security responsibilities within a representative enterprise AI system.
Learners can identify the components, trust boundaries and security ownership of an enterprise AI system before any application-layer detail is introduced.
Enterprise AI Application Security
Understanding how RAG, memory, data handling and APIs reshape the enterprise AI attack surface, and establishing a validated security baseline.
FocusUnderstand how retrieval-augmented generation changes what an AI application can access, and where that introduces new security surface.
Key learning areas- RAG architecture: retrieval, grounding and generation
- Vector stores, embeddings and knowledge-base design
- Retrieval boundaries and unauthorised-access risk
- Document-ingestion pipelines as a security entry point
- Distinguishing a model risk from an application or data risk
- Establishing a clean, evidenced application baseline before testing
A guided build of an enterprise-representative RAG application using controlled documents, followed by baseline validation of expected retrieval behaviour.
Learners can explain how RAG reshapes an AI application's attack surface and can validate and evidence a clean security baseline.
FocusExtend the enterprise AI security baseline to conversational memory, sensitive-data handling and the APIs that connect AI systems to the wider enterprise.
Key learning areas- Conversation state and persistent memory design
- AI data classification and handling of sensitive information
- API security, authentication and authorisation for AI-enabled services
- Approval workflows and audit-event design
- Data and authorisation boundaries across AI application components
- Evidence capture for later security comparison
A guided exercise extending the baseline application with memory, data-handling and API interactions, then documenting the resulting security posture.
Learners can recognise data and authorisation boundaries across a full enterprise AI application and preserve a defensible baseline for later assessment.
Agentic AI & MCP Security
Securing autonomous, tool-using agents: identity, delegated authority, least privilege and MCP trust boundaries.
FocusUnderstand what changes, from a security perspective, when an AI system can select capabilities and take action rather than only generate text.
Key learning areas- Agentic AI architecture and autonomous capability selection
- Tool-enabled workflows and action-taking AI systems
- Read versus write capability and the risk difference between them
- Autonomy levels and appropriate human-in-the-loop control points
- Early identification of excessive-agency risk
- Governance considerations for agent actions
A guided assessment of a controlled agentic AI environment, evaluating how capability selection and action execution actually behave.
Learners can explain agentic AI architecture and identify where autonomous action introduces new security responsibility.
FocusExamine how identity, delegated authority and the Model Context Protocol define trust between users, agents and connected tools.
Key learning areas- User identity versus agent identity, and delegated authority
- Least-privilege design for autonomous agents
- MCP clients, servers, tools and resources
- Trust and secure context exchange between agents and tools
- Approvals, monitoring and governance of agent actions
- Recommending controls for connected-tool ecosystems
A guided evaluation of a controlled Agentic AI and MCP environment, assessing trust, authority and access-boundary design.
Learners can assess an Agent → MCP → Tool architecture and recommend proportionate authority and monitoring controls.
AI Threat Modeling & Security Test Planning
Converting architecture understanding into structured threat models and authorised, evidence-driven test plans.
FocusConvert architectural understanding of an AI system into a structured threat model that identifies credible, prioritised risk.
Key learning areas- Assets, data flows, entry points and trust boundaries in AI systems
- AI-specific threat modeling using structured security methods
- RAG, memory, agent, MCP, identity and API risk within a single model
- Third-party and supply-chain risk considerations
- Prioritising risk by architecture and business impact
- Aligning threat models to recognised industry frameworks
A guided threat-modeling exercise producing a structured, evidence-ready threat model for a representative enterprise AI system.
Learners can produce an AI-focused threat model and prioritise findings by business impact rather than technical novelty.
FocusTranslate a threat model into a defensible, authorised security-test plan before any testing activity begins.
Key learning areas- Translating credible threats into testable hypotheses
- Defining authorised scope, rules of engagement and evidence requirements
- Security objectives and success criteria for AI assessments
- Ethical and legal considerations in AI security testing
- Evidence-handling and chain-of-custody principles
- Planning repeatable versus one-time evaluation activities
A guided planning exercise producing a scoped, authorised test plan derived directly from the prior week's threat model.
Learners can define defensible security-test cases and authorised scope before testing begins: the professional standard for AI security assessment.
Offensive AI Security & Red Teaming
Controlled, authorised adversarial assessment of prompt, retrieval, agent, tool and API surfaces with defensible evidence.
FocusBegin authorised, controlled adversarial assessment of an AI application's attack surface, starting with prompt and retrieval risk.
Key learning areas- AI attack-surface reconnaissance and assessment methodology
- Prompt and indirect-instruction risk categories
- RAG, retrieval and vector-store manipulation risk
- Memory-manipulation risk categories
- Maintaining scope, evidence and ethical controls throughout testing
- Distinguishing demonstrable weakness from anecdotal claims
Authorised adversarial testing exercises in a controlled AI cyber range, focused on prompt and retrieval-layer risk categories.
Learners can demonstrate AI security weaknesses at the prompt and retrieval layer with evidence suitable for root-cause analysis.
FocusExtend authorised adversarial assessment to agent, tool, MCP and API surfaces, and introduce repeatable evaluation concepts.
Key learning areas- Agent, tool and MCP abuse scenarios
- API abuse and authorisation-testing concepts for AI-enabled services
- Repeatable and automated AI security evaluation concepts
- Differentiating manual offensive testing from structured AI red teaming
- Evidence capture supporting root-cause and business-impact analysis
- Professional reporting standards for AI security findings
Authorised adversarial testing exercises in a controlled AI cyber range, focused on agent, tool, MCP and API risk categories.
Learners can differentiate manual testing from structured AI red teaming and capture evidence that supports defensible findings.
AI Security Detection & Defense
Designing detection and monitoring, implementing layered controls, and validating risk reduction through retesting.
FocusUse evidence from prior assessment activity to design meaningful detection and monitoring for AI-enabled workflows.
Key learning areas- Telemetry sources across prompt, retrieval, memory, agent, MCP and tool layers
- Designing detections that reflect real attack behaviour rather than noise
- Alert quality, triage considerations and false-positive management
- Monitoring requirements across the AI application stack
- Connecting detection design back to threat-model findings
- Detection-engineering documentation standards
A guided exercise designing detection and monitoring requirements using evidence captured during the prior month's assessment activity.
Learners can design useful AI security telemetry and detections grounded in demonstrated attack behaviour.
FocusImplement layered defensive controls at the correct trust boundary, then validate their effectiveness through retesting.
Key learning areas- Secure RAG, memory protection, agent identity and tool-authorisation controls
- Runtime policy enforcement, execution limits and approval controls
- Secure AI delivery and supply-chain awareness
- Security regression concepts for AI-enabled systems
- Original retest, modified bypass attempt and legitimate-workflow validation
- Residual-risk analysis after control implementation
A guided exercise implementing layered controls in response to prior findings, then retesting to confirm risk reduction and preserved business functionality.
Learners can implement layered AI security controls and prove their effectiveness through retesting and residual-risk analysis.
AI for Cybersecurity & Governance, Risk & Assurance
Using AI responsibly to support security operations, and translating technical evidence into enterprise governance and assurance decisions.
FocusUse AI responsibly as an accelerator for established cybersecurity workflows, with human validation built in throughout.
Key learning areas- AI-assisted log analysis and alert triage
- AI-assisted threat hunting and incident analysis
- Human-validation requirements and hallucination risk in security use cases
- Appropriate versus inappropriate use of AI in security operations
- Documenting AI-assisted analysis for audit and review
- Limits of AI reliability in high-stakes security decisions
A guided exercise using AI to support a controlled cybersecurity analysis workflow, with structured human validation of every output.
Learners can use AI responsibly to support cybersecurity analysis while maintaining accountable human judgement.
FocusTranslate technical AI security evidence into the governance, risk and assurance language enterprise decision-makers require.
Key learning areas- AI system inventory and risk-register practices
- Provider risk, privacy considerations and control mapping
- Alignment with recognised AI risk and assurance frameworks
- Production-readiness and assurance-evidence standards
- Residual-risk communication for non-technical stakeholders
- Building an evidence-backed AI risk and assurance package
A guided exercise converting a technical AI security assessment into a structured risk, assurance and production-readiness package.
Learners can translate technical AI security findings into governance and business-risk decisions defensible to an executive audience.
Capstone Integration Experience
Integrating the complete lifecycle into one defensible enterprise AI security assessment and executive presentation.
FocusReview the end-to-end architecture, threat model and assessment plan for the capstone scenario before finalising testing and remediation.
Key learning areas- A structured review checklist spanning the full program lifecycle
- Common integration gaps across architecture, threat model and test scope
- Running a staged review process with checkpoints
- Presenting technical security reasoning to a structured review panel
- Refining the assessment and remediation plan based on feedback
A staged review process: present the capstone architecture, threat model and test plan for structured feedback, then revise before proceeding to final testing and remediation.
Learners can identify and close assessment and remediation gaps before they become costly to fix.
FocusComplete the capstone assessment lifecycle and deliver a professional technical report and executive security presentation.
Key learning areas- Finalising evidence, retesting and residual-risk assessment
- Technical report structure and evidence packaging
- Presenting security decisions to an executive-level audience
- Incorporating structured feedback under a deadline
- Mapping completed capability to professional AI security roles
A final assessment, retest and reporting cycle, followed by a timed oral security presentation and executive Q&A.
Learners leave with a defensible, evidence-backed AI security assessment and the ability to present it to both technical and executive audiences.
Hands-on labs
AI, LLM & Cybersecurity Foundations Lab
Work hands-on in a controlled AI environment to observe real model behaviour and map it onto core cybersecurity principles and enterprise AI architecture.
- Baseline LLM behaviour observation and instruction analysis
- Trust-boundary and asset identification in a representative AI system
- Mapping cybersecurity fundamentals onto AI-enabled architecture
Outcome. A documented architecture and trust-boundary walkthrough of a representative enterprise AI system.
Enterprise AI Application Security Baseline Lab
Build and validate a clean, evidenced security baseline for an enterprise AI application spanning RAG, memory, data handling and APIs.
- RAG and knowledge-base security configuration
- Conversation memory and AI data-handling review
- API authentication, authorisation and audit-event validation
Outcome. A fully evidenced enterprise AI application baseline, ready for later security comparison.
Agentic AI & MCP Security Lab
Assess a connected, tool-using AI agent environment to evaluate identity, delegated authority and MCP trust boundaries.
- Agent capability-selection and action-execution assessment
- Identity, delegated-authority and least-privilege evaluation
- MCP trust and connected-tool ecosystem review
Outcome. A documented trust-and-authority assessment of an Agent → MCP → Tool architecture.
AI Threat Modeling & Test Planning Lab
Produce a structured AI threat model and translate it into an authorised, evidence-driven security-test plan.
- Structured AI-specific threat modeling
- Risk prioritisation by architecture and business impact
- Authorised scope and test-hypothesis definition
Outcome. A defensible threat model and authorised test plan, ready for controlled testing.
Offensive AI Security & Red-Teaming Lab
Conduct authorised adversarial testing in a controlled AI cyber range across prompt, retrieval, agent, tool, MCP and API surfaces.
- Authorised adversarial testing methodology
- Evidence capture for root-cause and impact analysis
- Differentiating manual testing from structured AI red teaming
Outcome. An evidence-backed record of demonstrated AI security weaknesses across the assessed surfaces.
AI Detection & Defensive Engineering Lab
Design detection and monitoring from prior evidence, implement layered controls, then retest to confirm risk reduction.
- AI security telemetry and detection design
- Layered defensive-control implementation
- Retesting and residual-risk validation
Outcome. A validated set of detective and defensive controls with confirmed risk reduction through retesting.
AI-Enabled Security Operations & Governance Lab
Use AI responsibly to support a cybersecurity workflow, then convert the resulting technical evidence into a governance and assurance package.
- AI-assisted log analysis, triage and threat hunting with human validation
- AI risk-register and control-mapping construction
- Assurance-evidence and executive-risk communication
Outcome. An evidence-backed AI risk and assurance package, ready for executive review.
Enterprise Ai Security Assurance Capstone
Step into the role of enterprise AI security assessor for a fictional organisation operating several interconnected AI systems, and deliver one coherent, end-to-end security assessment, from architecture review through governance sign-off, that a real security or executive committee could act on.
- End-to-end AI architecture and threat-model review
- Authorised assessment, detection design and defensive-control validation
- AI-assisted security-operations judgement
- Governance, risk and assurance packaging
- Executive-level technical communication
Outcome. A reviewed, presentation-ready enterprise AI security assessment package, and the ability to defend both technical evidence and business-risk conclusions to an executive audience.
The capstone runs across the final two weeks of the program: one week to review architecture, threat model and test plan under structured feedback, and one week to complete assessment, remediation validation, and deliver a stakeholder-ready oral security presentation with live executive Q&A.
- Real industry projects drawn from Quantum's client and industry engagements
- Teams build against real requirements and deadlines, with mentor reviews and a final demo
Learners who complete the first six months and meet the program's attendance and assessment requirements move into a six-month Employment Training Programme in a production environment.
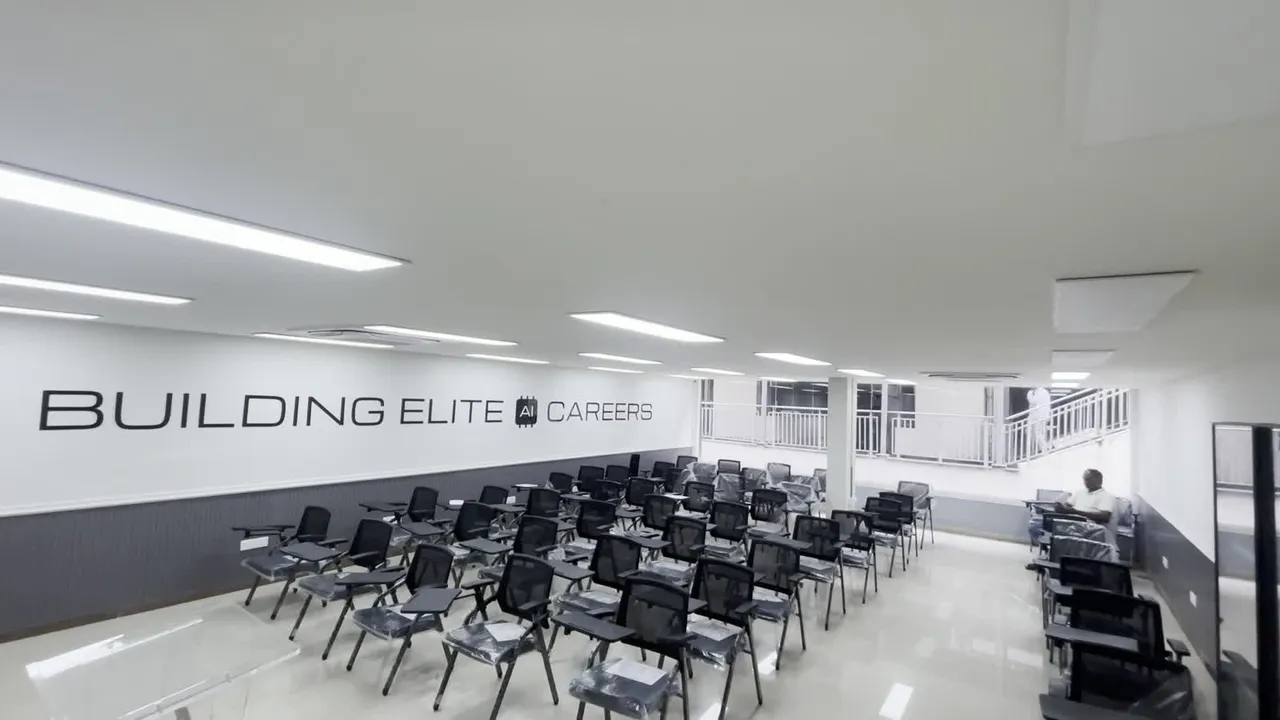
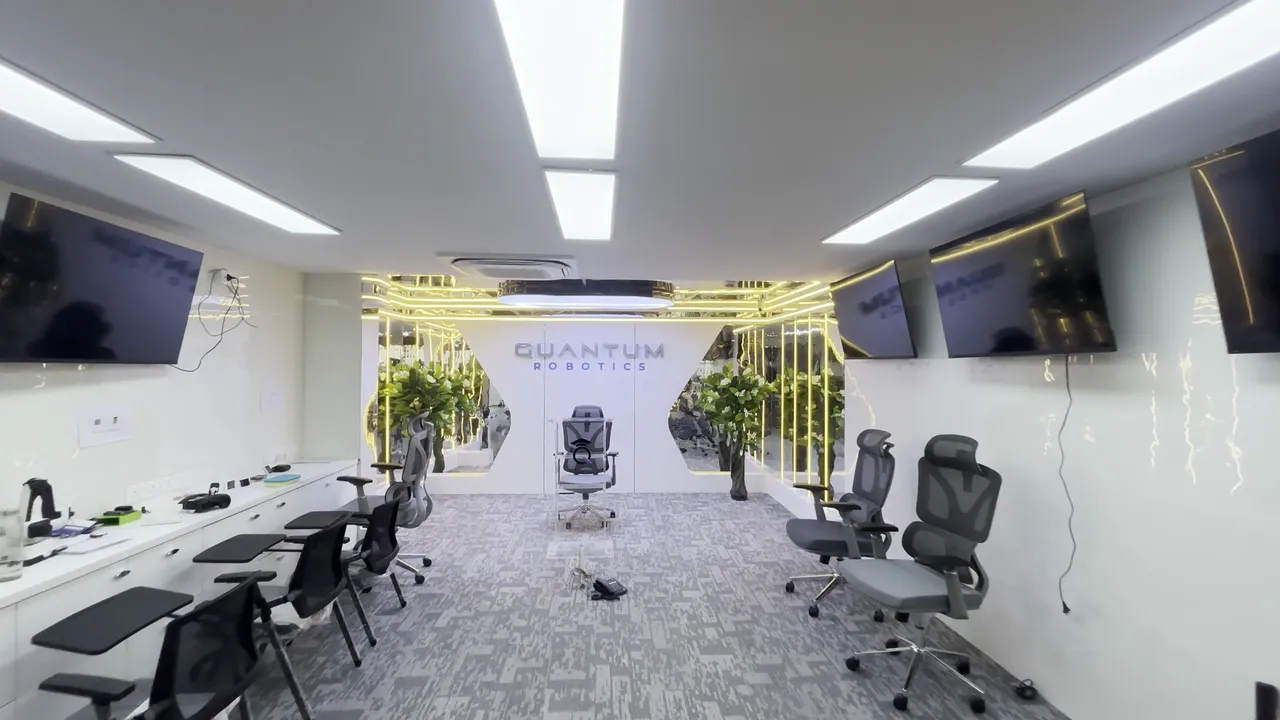
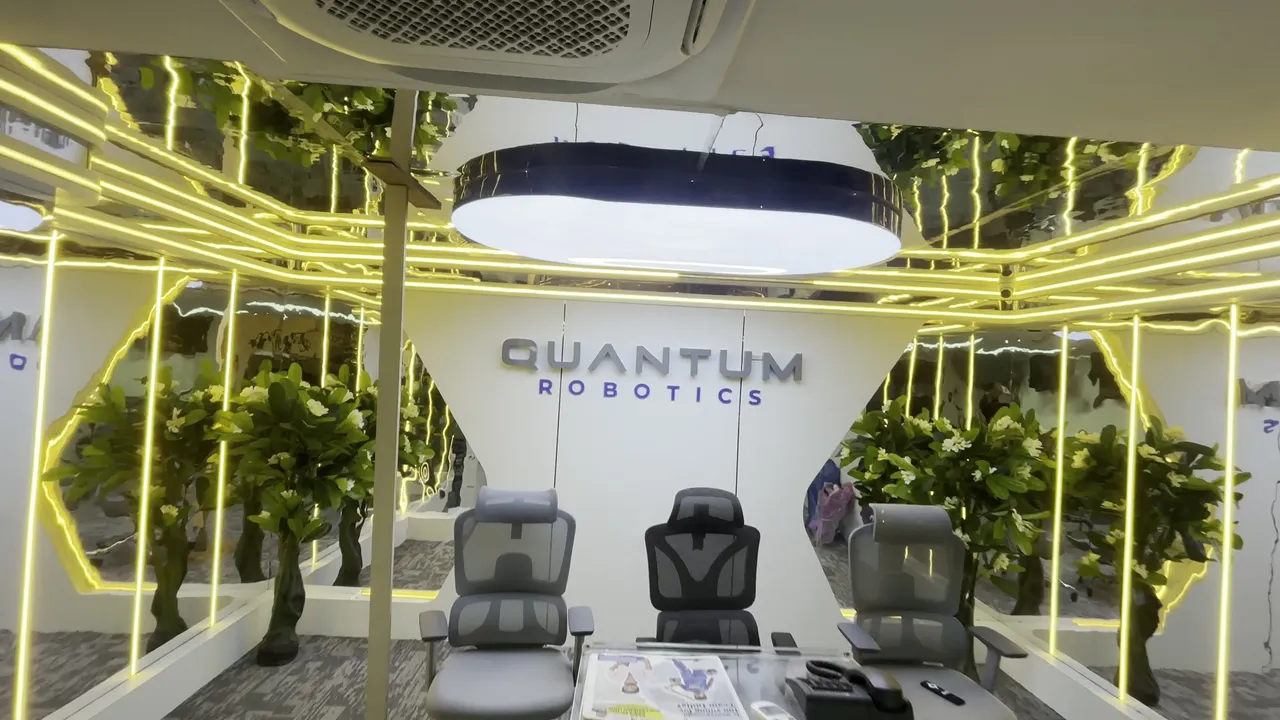
The campus, Jubilee Hills.
Classrooms, a robotics lab and rooms named after the pioneers. Inaugural batches sit here in person.
Ready to join the next batch?
Train the way Hyderabad hires: project-first, certification-aligned and reviewed by people who do this for a living.
Book a free demo